

Get Ready with NSE5_FCT-7.0 Exam Dumps (2024)
Realistic NSE5_FCT-7.0 Dumps are Available for Instant Access
Fortinet NSE5_FCT-7.0 (Fortinet NSE 5 - FortiClient EMS 7.0) exam is a certification program that aims to test the skills and knowledge of IT professionals in managing and configuring FortiClient EMS 7.0. NSE5_FCT-7.0 exam is designed for individuals who have experience in IT security and want to enhance their skills in endpoint security management.
NEW QUESTION # 21
Refer to the exhibit.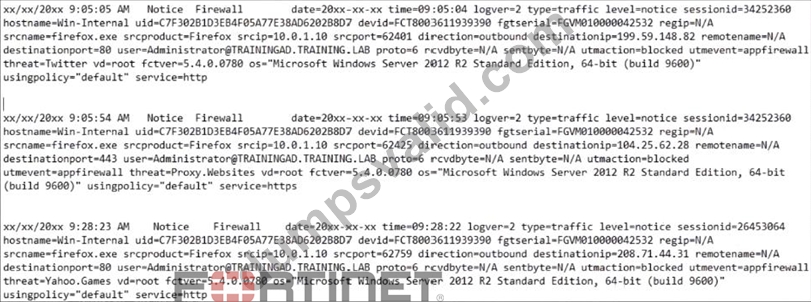
Based on the FortiClient logs shown in the exhibit which application is blocked by the application firewall?
- A. Facebook
- B. Internet Explorer
- C. Twitter
- D. Firefox
Answer: D
NEW QUESTION # 22
Refer to the exhibit.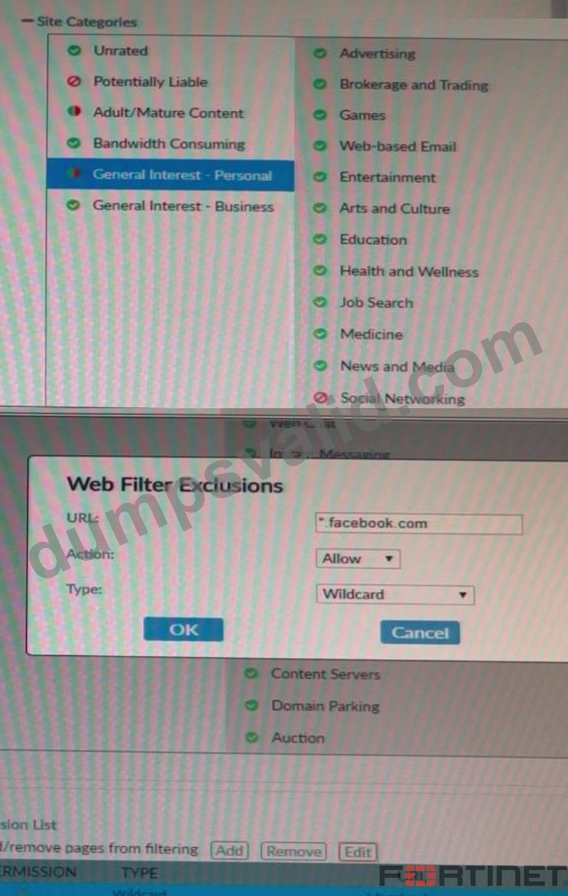
Based on the settings shown in the exhibit, which action will FortiClient take when users try to access www.facebook.com?
- A. FortiClient will block access to Facebook and its subdomains.
- B. FortiClient will allow access to Facebook
- C. FortiClient will prompt a warning message to warn the user before they can access the Facebook website
- D. FortiClient will monitor only the user's web access to the Facebook website
Answer: B
NEW QUESTION # 23
Refer to the exhibit.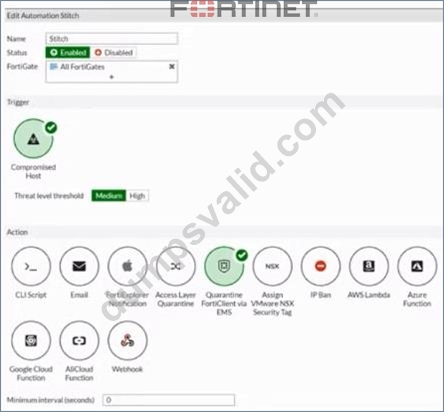
Based on the Security Fabric automation settings, what action will be taken on compromised endpoints?
- A. Endpoints will be quarantined through EMS
- B. Endpoints will be banned on FortiGate
- C. An email notification will be sent for compromised endpoints
- D. Endpoints will be quarantined through FortiSwitch
Answer: A
NEW QUESTION # 24
Refer to the exhibit, which shows the endpoint summary information on FortiClient EMS.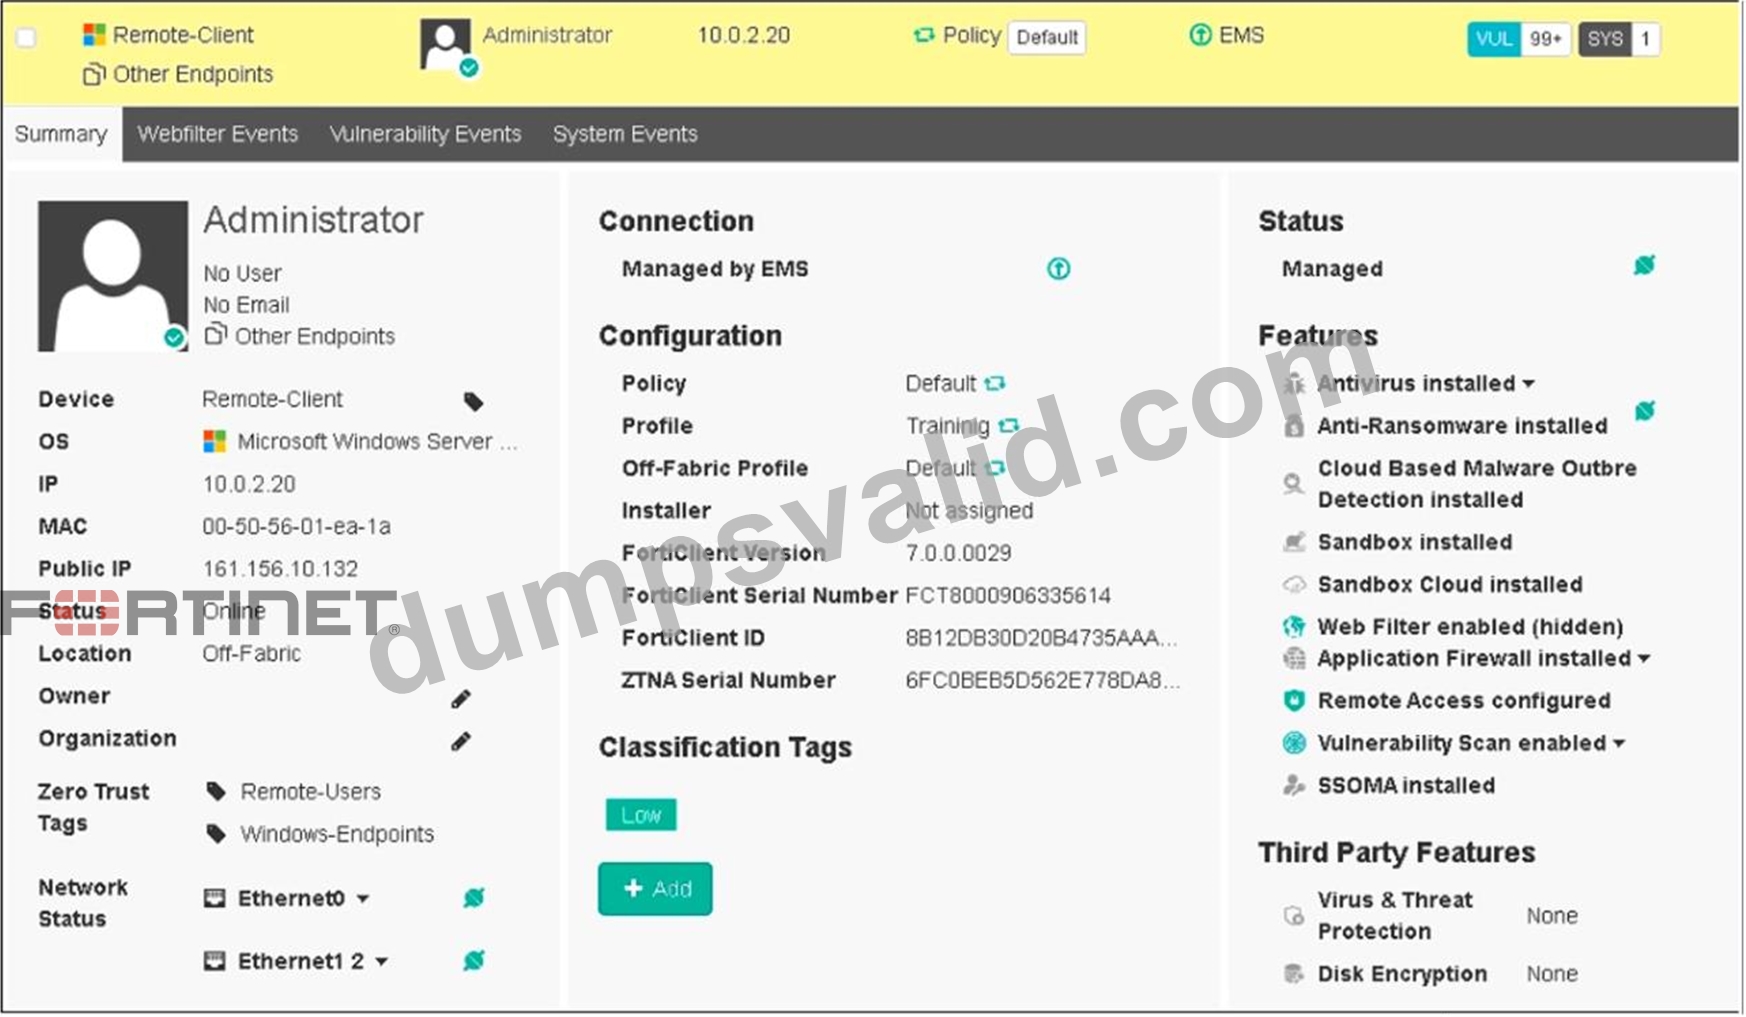
What two conclusions can you make based on the Remote-Client status shown above? (Choose two.)
- A. The endpoint is currently off-net.
- B. The endpoint has been assigned the Default endpoint policy.
- C. The endpoint is classified as at risk.
- D. The endpoint is configured to support FortiSandbox.
Answer: A,B
NEW QUESTION # 25
Refer to the exhibit.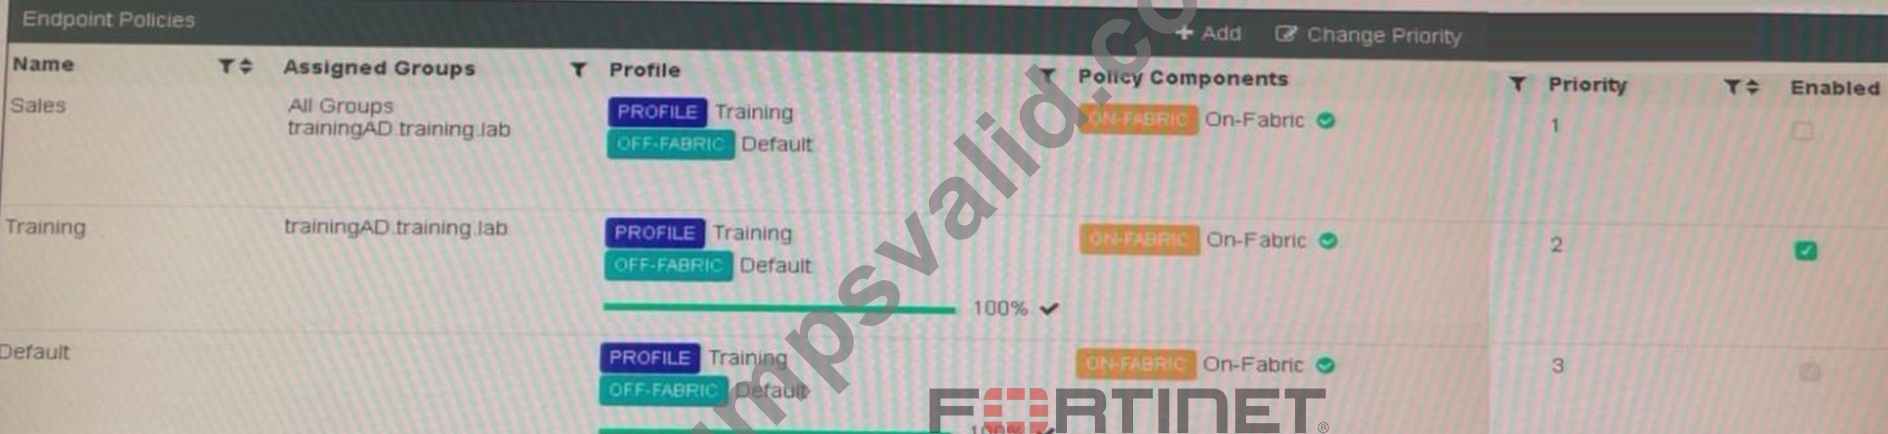
Which shows multiple endpoint policies on FortiClient EMS.
Which policy is applied to the endpoint in the AD group trainingAD?
- A. The Default policy because it has the highest priority
- B. Both the Sales and Training policies because their priority is higher than the Default policy
- C. The Training policy
- D. The Sales policy
Answer: C
NEW QUESTION # 26
Which two statements are true about ZTNA? (Choose two.)
- A. ZTNA provides a security posture check
- B. ZTNA manages access through the client only
- C. ZTNA provides role-based access
- D. ZTNA manages access for remote users only
Answer: A,C
NEW QUESTION # 27
Refer to the exhibit.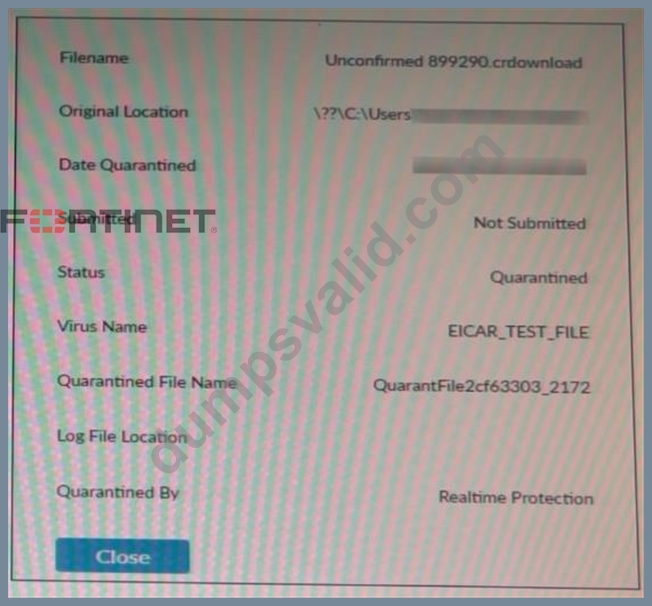
Based on the FortiClient log details shown in the exhibit, which two statements are true? (Choose two.)
- A. The file status is Quarantined
- B. The filename is sent to ForuSandbox for further inspection.
- C. The filename is Unconfirmed 899290 .crdownload.
- D. The file location IS \??\D:\Users\.
Answer: A,C
NEW QUESTION # 28
Refer to the exhibit.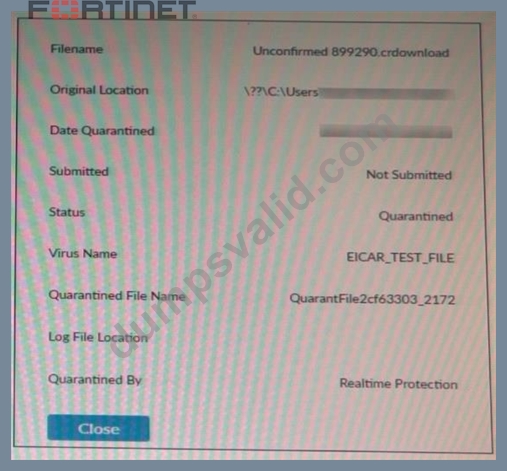
Based on the FortiClient log details shown in the exhibit, which two statements are true? (Choose two.)
- A. The file status is Quarantined
- B. The filename is sent to ForuSandbox for further inspection.
- C. The filename is Unconfirmed 899290 .crdownload.
- D. The file location IS \??\D:\Users\.
Answer: A,C
NEW QUESTION # 29
An administrator is required to maintain a software vulnerability on the endpoints, without showing the feature on the FortiClient dashboard. What must the administrator do to achieve this requirement?
- A. Click the hide icon on the vulnerability scan tab
- B. Disable select the vulnerability scan feature in the deployment package
- C. Select the vulnerability scan feature in the deployment package, but disable the feature on the endpoint profile
- D. Use the default endpoint profile
Answer: A
NEW QUESTION # 30
Refer to the exhibit.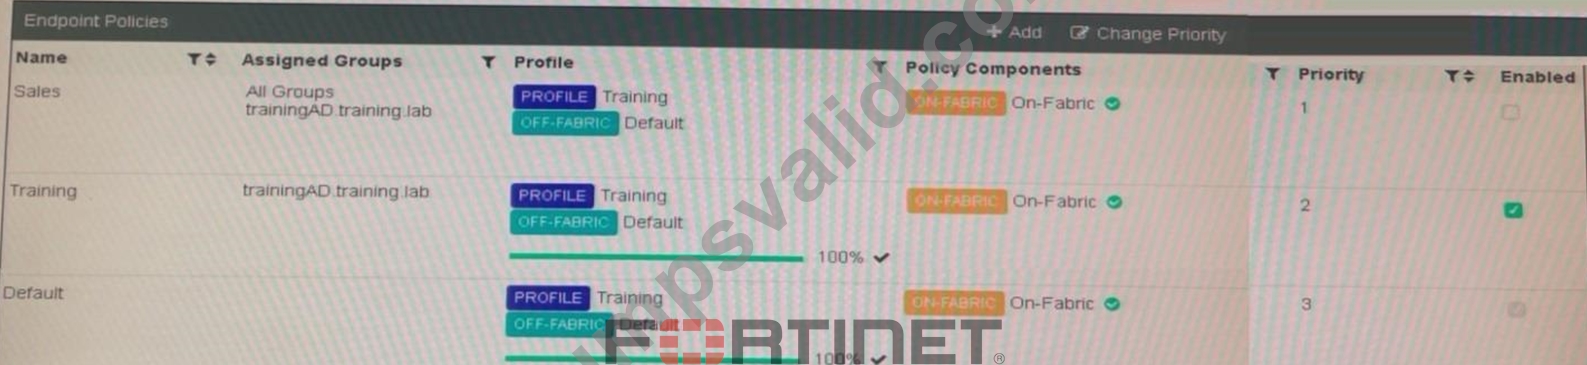
Which shows multiple endpoint policies on FortiClient EMS.
Which policy is applied to the endpoint in the AD group trainingAD?
- A. The Default policy because it has the highest priority
- B. Both the Sales and Training policies because their priority is higher than the Default policy
- C. The Training policy
- D. The Sales policy
Answer: C
NEW QUESTION # 31
Refer to the exhibits.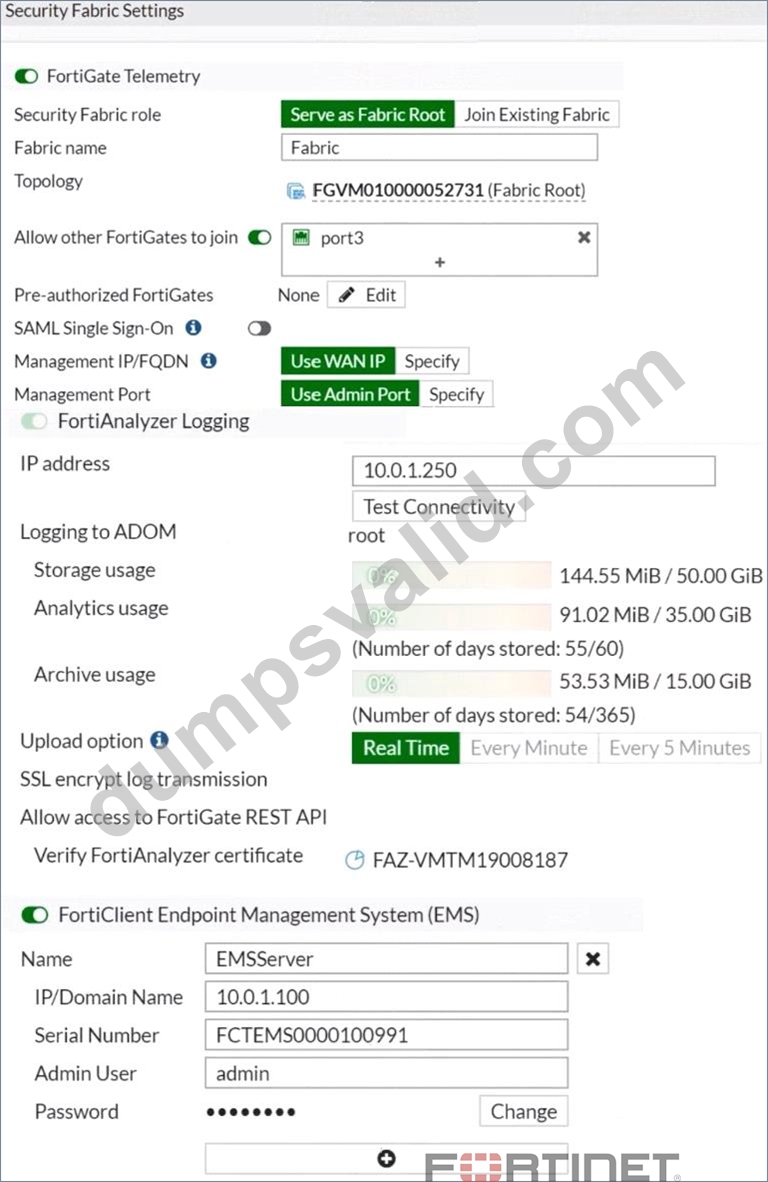
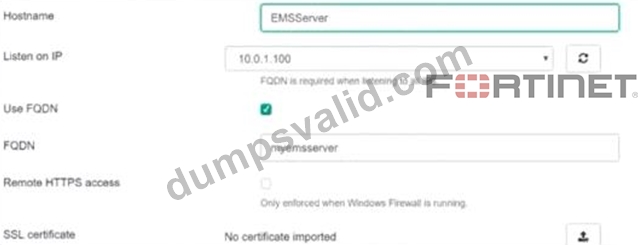
Based on the FortiGate Security Fabric settings shown in the exhibits, what must an administrator do on the EMS server to successfully quarantine an endpoint. when it is detected as a compromised host (loC)?
- A. The administrator must enable SSH access to EMS.
- B. The administrator must enable remote HTTPS access to EMS.
- C. The administrator must authorize FortiGate on FortiAnalyzer.
- D. The administrator must enable FQDN on EMS.
Answer: B
NEW QUESTION # 32
Refer to the exhibit.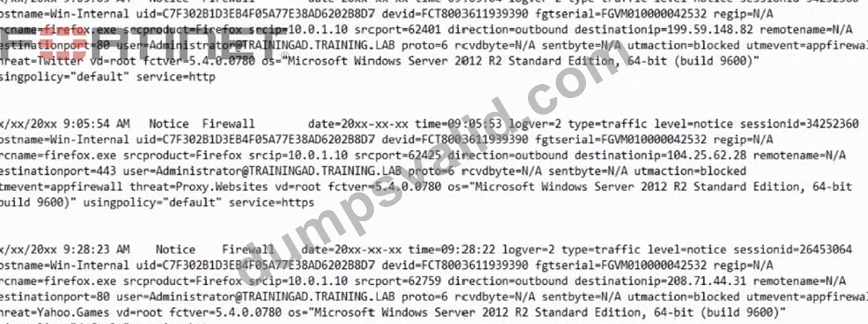
Based on the FortiClient logs shown in the exhibit which application is blocked by the application firewall?
- A. Facebook
- B. Internet Explorer
- C. Twitter
- D. Firefox
Answer: D
NEW QUESTION # 33
Which two third-party tools can an administrator use to deploy FortiClient? (Choose two.)
- A. Microsoft Windows Installer
- B. QR code generator
- C. Microsoft SCCM
- D. Microsoft Active Directory GPO
Answer: C,D
NEW QUESTION # 34
A FortiClient EMS administrator has enabled the compliance rule for the sales department. Which Fortinet device will enforce compliance with dynamic access control?
- A. FortiClient
- B. FortiGate
- C. FortiClient EMS
- D. FortiAnalyzer
Answer: B
NEW QUESTION # 35
Which two statements are true about the ZTNA rule? (Choose two. )
- A. It redirects the client request to the access proxy
- B. It defines the access proxy
- C. It enforces access control
- D. It applies security profiles to protect traffic
Answer: C,D
Explanation:
"A ZTNA rule is a proxy policy used to enforce access control. ZTNA tags or tag groups can be defined to enforce zero trust role based access. Security profiles can be configured to protect this traffic."
"ZTNA rules help control access by defining users and ZTNA tags to perform user authentication and security posture checks. And just like firewall policies, you can control the source and destination addresses, and apply appropriate security profiles to scan the traffic." https://docs.fortinet.com/document/fortigate/7.0.0/ztna-deployment/899992/configuring-ztna-rules-to-control-access
NEW QUESTION # 36
Which statement about FortiClient comprehensive endpoint protection is true?
- A. It helps to safeguard systems from data loss.
- B. lt helps to safeguard systems from advanced security threats, such as malware.
- C. It helps to safeguard systems from DDoS.
- D. It helps to safeguard systems from email spam
Answer: B
Explanation:
FortiClient provides comprehensive endpoint protection for your Windows-based, Mac-based, and Linuxbased desktops, laptops, file servers, and mobile devices such as iOS and Android. It helps you to safeguard your systems with advanced security technologies, all of which you can manage from a single management console.
NEW QUESTION # 37
Refer to the exhibits.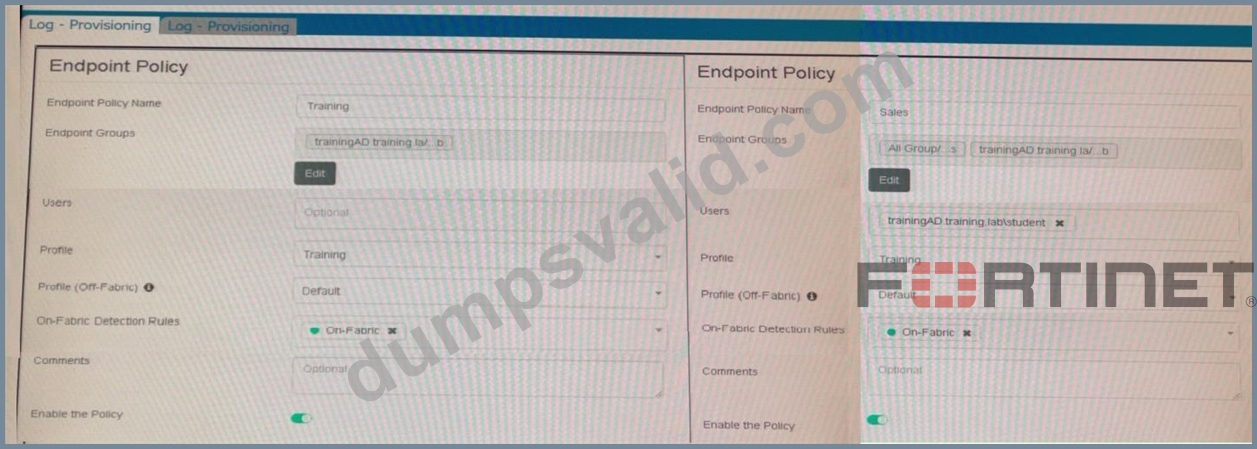
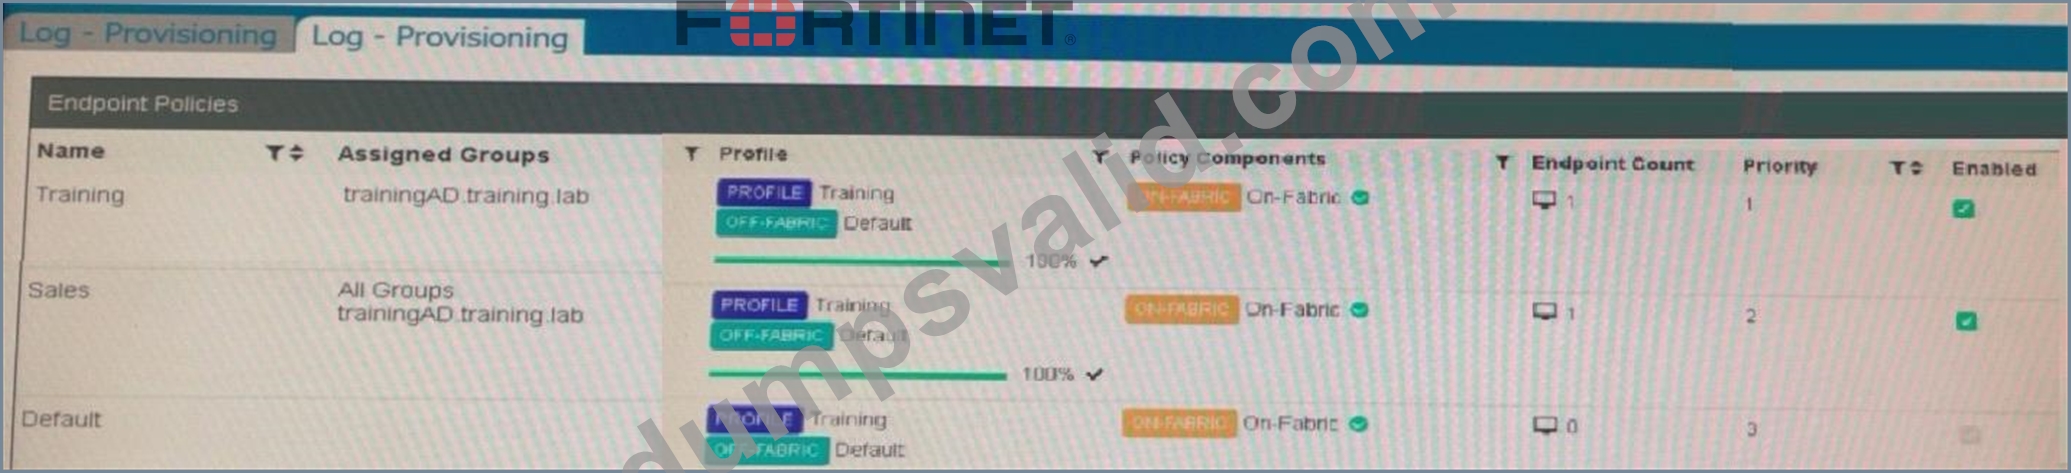
Which shows the configuration of endpoint policies.
Based on the configuration, what will happen when someone logs in with the user account student on an endpoint in the trainingAD domain?
- A. FortiClient EMS will assign the Training policy
- B. FortiClient EMS will assign the Sales policy
- C. FortiClient EMS will assign the Training policy for on-fabric endpoints and the Sales policy for the off-fabric endpoint
- D. FortiClient EMS will assign the Default policy
Answer: D
NEW QUESTION # 38
An administrator needs to connect FortiClient EMS as a fabric connector to FortiGate. What is the prerequisite to get FortiClient EMS to connect to FortiGate successfully?
- A. Import and verify the FortiClient client certificate on FortiGate.
- B. Revoke and update the FortiClient client certificate on EMS.
- C. Import and verify the FortiClient EMS root CA certificate on FortiGate
- D. Revoke and update the FortiClient EMS root CA.
Answer: A
NEW QUESTION # 39
Refer to the exhibits.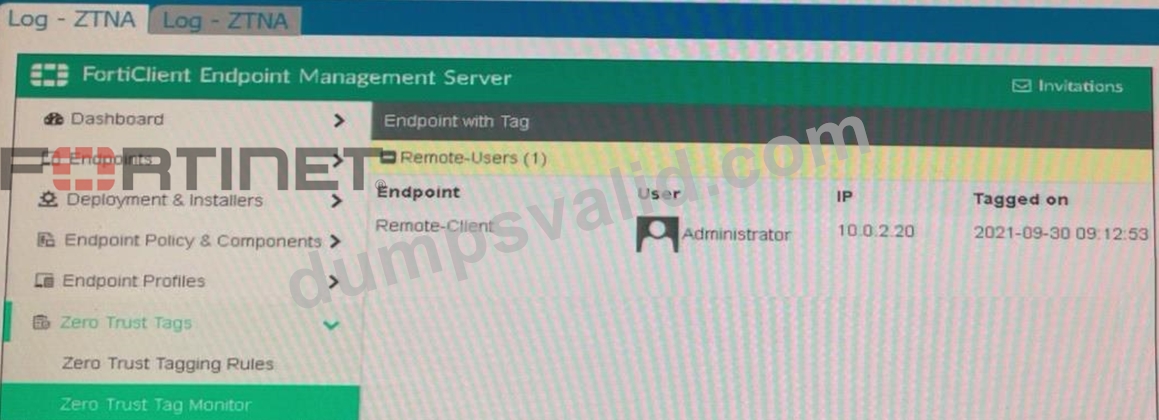
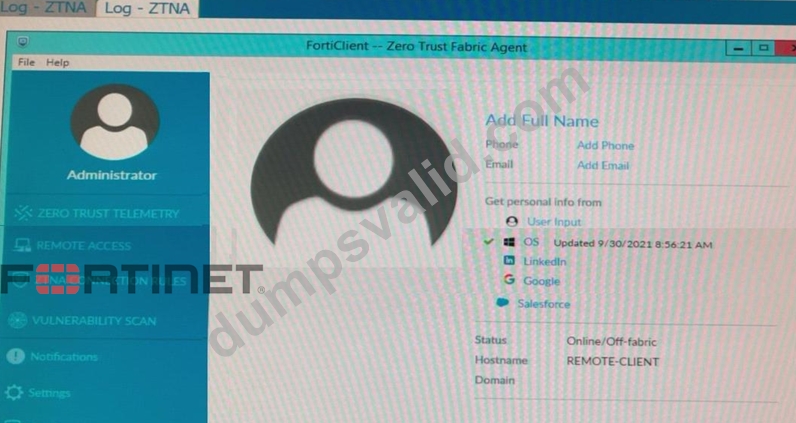
Which show the Zero Trust Tag Monitor and the FortiClient GUI status.
Remote-Client is tagged as Remote-Users on the FortiClient EMS Zero Trust Tag Monitor.
What must an administrator do to show the tag on the FortiClient GUI?
- A. Change the endpoint control setting to enable tag visibility
- B. Update tagging rule logic to enable tag visibility
- C. Change the FortiClient system settings to enable tag visibility
- D. Change the user identity settings to enable tag visibility
Answer: A
NEW QUESTION # 40
Refer to the exhibit.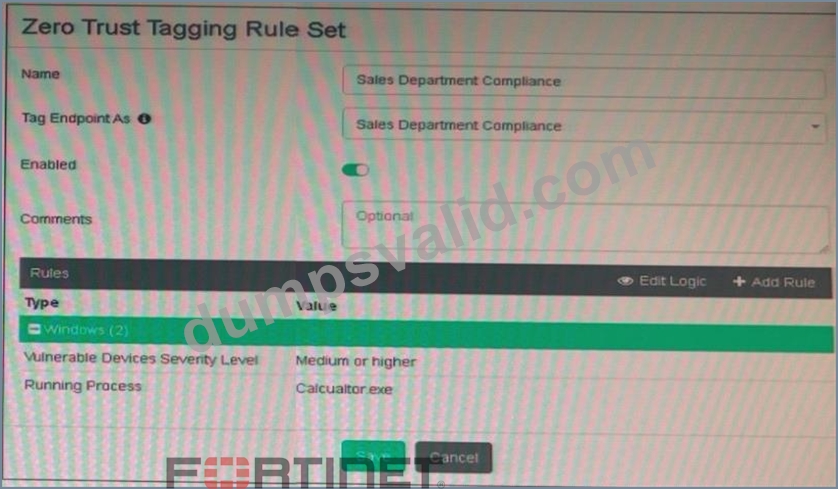
Based on the settings shown in the exhibit, which two actions must the administrator take to make the endpoint compliant? (Choose two.)
- A. Enable the webfilter profile
- B. Run Calculator application on the endpoint
- C. Integrate FortiSandbox for infected file analysis
- D. Patch applications that have vulnerability rated as high or above
Answer: B,D
NEW QUESTION # 41
Refer to the exhibits.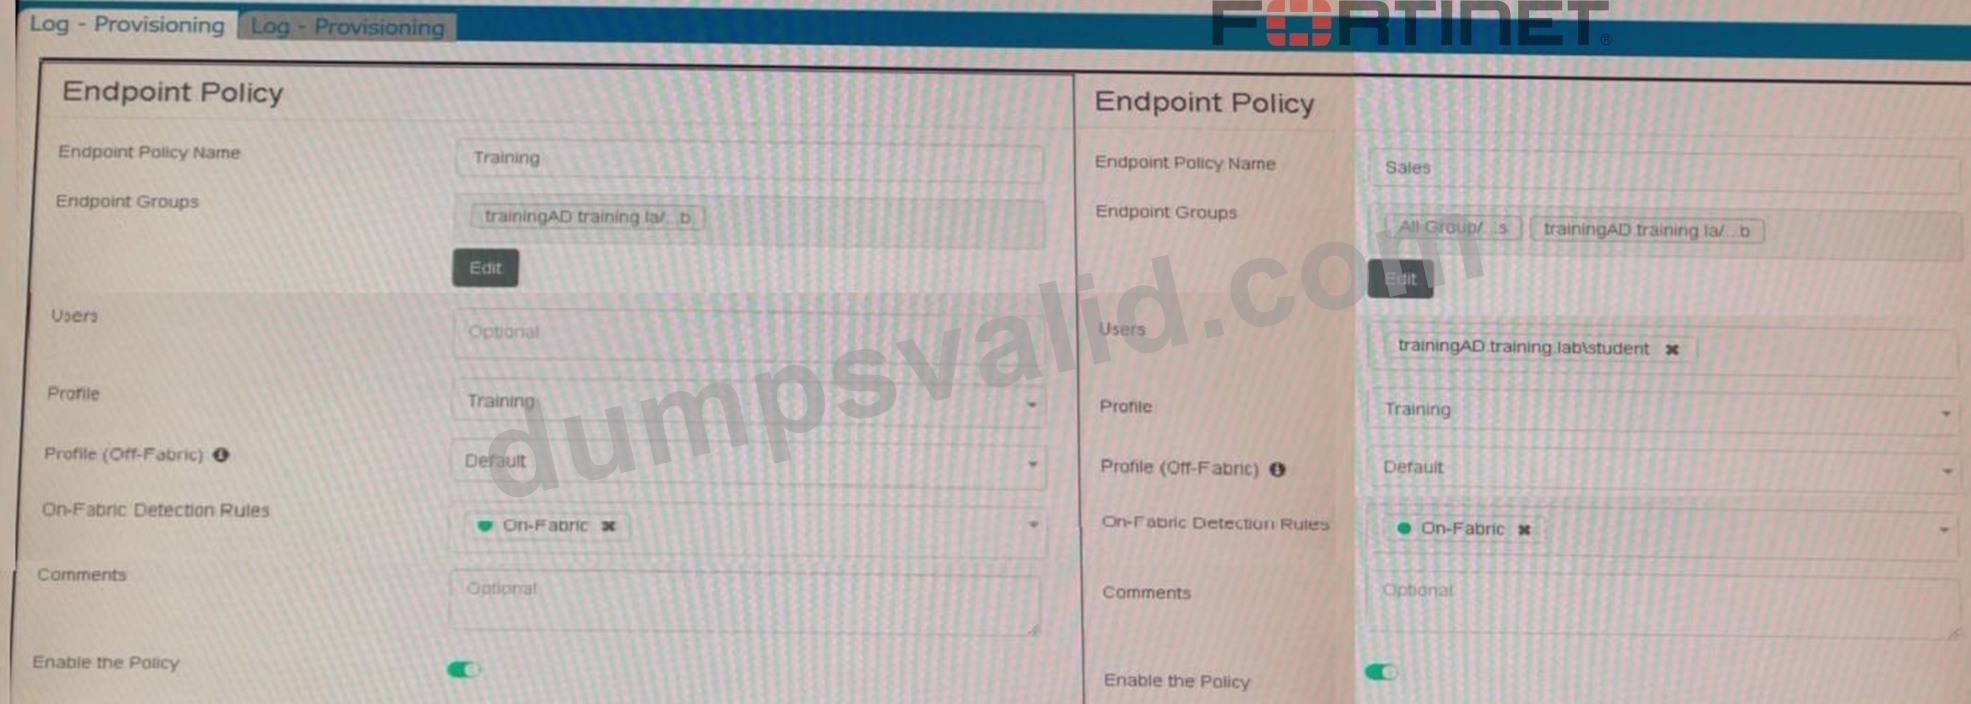
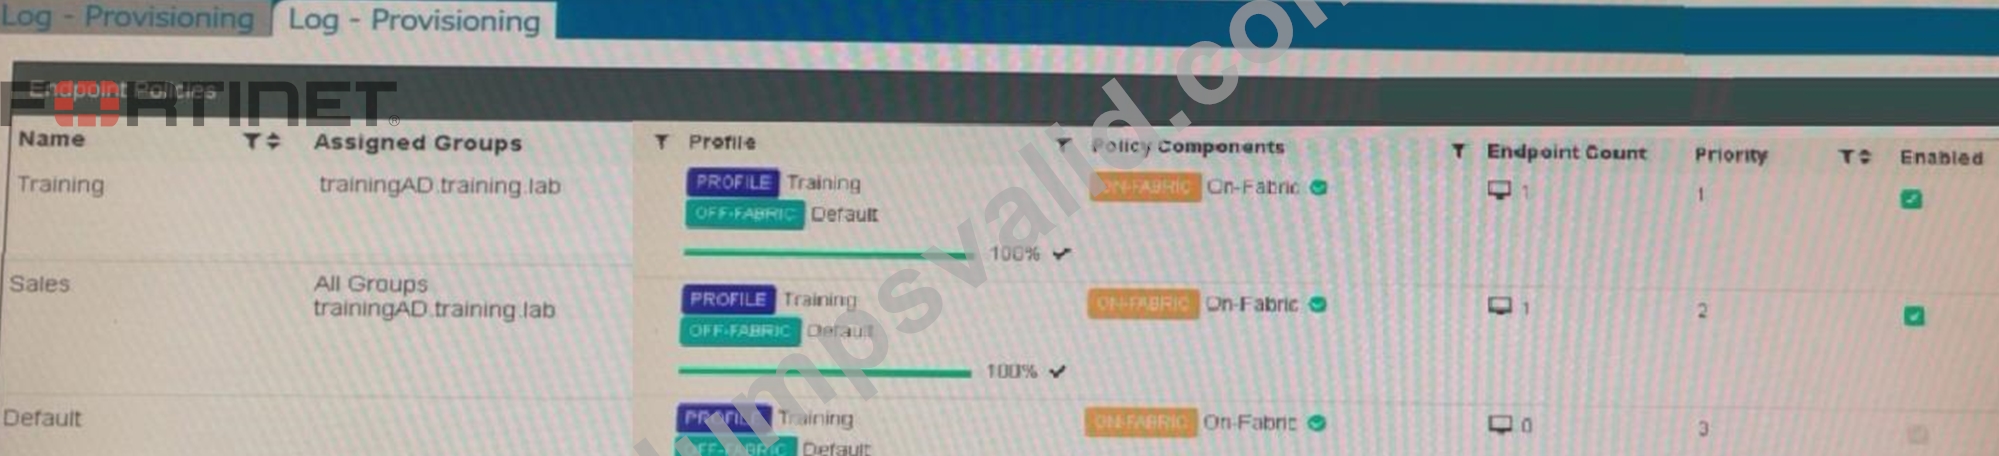
Which shows the configuration of endpoint policies.
Based on the configuration, what will happen when someone logs in with the user account student on an endpoint in the trainingAD domain?
- A. FortiClient EMS will assign the Sales policy
- B. FortiClient EMS will assign the Default policy
- C. FortiClient EMS will assign the Training policy for on-fabric endpoints and the Sales policy for the off-fabric endpoint
- D. FortiClient EMS will assign the Training policy
Answer: D
NEW QUESTION # 42
Which security fabric component sends a notification to quarantine an endpoint after IOC detection in the automation process?
- A. FortiClient
- B. Forti Gate
- C. FortiAnalyzer
- D. ForbClient EMS
Answer: B
NEW QUESTION # 43
What is the function of the quick scan option on FortiClient?
- A. It performs a full system scan including all files, executable files, DLLs, and drivers for threats.
- B. It scans executable files, DLLs, and drivers that are currently running, for threats.
- C. It allows users to select a specific file folder on their local hard disk drive (HDD), to scan for threats.
- D. It scans programs and drivers that are currently running, for threats.
Answer: D
NEW QUESTION # 44
......
Fortinet NSE5_FCT-7.0 certification is ideal for individuals who are responsible for managing and maintaining FortiClient EMS 7.0 in their organizations. This includes network administrators, security professionals, and IT managers who need to ensure that client endpoints are secure, up-to-date, and compliant with company policies. Fortinet NSE 5 - FortiClient EMS 7.0 certification exam is also appropriate for individuals who want to enhance their career prospects by demonstrating their expertise in Fortinet technologies. Earning the Fortinet NSE5_FCT-7.0 certification can help IT professionals stand out in the job market and increase their earning potential. Furthermore, the certification is a prerequisite for the Fortinet NSE 5 certification, which is a higher-level certification that demonstrates advanced knowledge and skills in Fortinet technologies.
Download Exam NSE5_FCT-7.0 Practice Test Questions with 100% Verified Answers: https://examcollection.dumpsvalid.com/NSE5_FCT-7.0-brain-dumps.html